Buy kopa-houtskooloven.be ?
We are moving the project
kopa-houtskooloven.be .
Are you interested in purchasing the domain
kopa-houtskooloven.be ?
domain@kv-gmbh.de · 0541-91531010
Buy kopa-houtskooloven.be ?
What is BitLocker TPM?
BitLocker TPM (Trusted Platform Module) is a security feature in Windows operating systems that uses a hardware component called TPM to provide enhanced protection for data stored on a computer's hard drive. TPM is a microchip that securely stores encryption keys, passwords, and other sensitive information to help protect against unauthorized access to the system. When BitLocker TPM is enabled, the encryption keys are securely stored in the TPM, making it more difficult for attackers to access the data even if they physically remove the hard drive from the computer. **
Can't you activate TPM?
Yes, TPM (Trusted Platform Module) can be activated on compatible devices through the device's BIOS settings. However, not all devices have TPM built-in, so it's important to check the device's specifications to see if TPM is available. Once activated, TPM provides hardware-based security features such as secure boot, device encryption, and key management to help protect sensitive data and ensure the integrity of the system. **
Similar search terms for Tpm
Top-Angebote
Products related to Tpm:
-
vidaXL Tapis de cuisine lavable texte Cooking 45x150 cm veloursCe tapis de cuisine est extrêmement doux et moelleux, et son design élégant attire tous les regards dans votre intérieur. Matériau durable : le dessus du tapis de cuisine est recouvert d'un tissu de velours doux qui absorbe rapidement l'eau et la saleté. La base en latex antidérapante assure que le tapis de cuisine adhère fermement au sol pour plus de sécurité. Lavable en machine : vous pouvez facilement nettoyer le tapis de sol de cuisine car il est lavable en machine. Rangement pratique : le tapis est flexible et peut être facilement enroulé pour le rangement et le transport.23,80 €*Shipping: 0,00 €Secure redirect to the provider
-
Smoking Hot van Kilian Uniseks Eau de Parfum 50mlSmoking Hot van By Kilian is een Oriëntaalse Kruidige geur voor dames en heren. Dit is een nieuwe geur. Smoking Hot werd gelanceerd in 2023. De neus achter deze geur is Mathieu Nardin. Topnoten zijn Appel, Kaneel en Rook; hartnoten zijn Tabak, Vanille en Mos; basisnoten zijn Bourbon Vanille, Orcanoxandtrade;, Zoethout, Iso E Super en Muskaatsalie.185,00 €*Shipping: 0,00 €Secure redirect to the provider
-
bdk Parfums Rouge Smoking Eau de Parfum mixte 50 mlbdk Parfums Rouge Smoking, 50 ml, Eaux de Parfum mixte, Fraîche et mystérieuse, moderne et à la fois hors du temps ! Il s'agit bien de l'eau de parfum mixte bdk Parfums Rouge Smoking dont la composition parfumée est parfaite pour les femmes comme pour les hommes. pour celles et ceux qui n'ont pas peur de sortir des sentiers battus pour les femmes comme pour les hommes125,60 €*Shipping: 3,45 €Secure redirect to the provider
-
bdk Parfums Rouge Smoking Eau de Parfum mixte 10 mlbdk Parfums Rouge Smoking, 10 ml, Eaux de Parfum mixte, Fraîche et mystérieuse, moderne et à la fois hors du temps ! Il s'agit bien de l'eau de parfum mixte bdk Parfums Rouge Smoking dont la composition parfumée est parfaite pour les femmes comme pour les hommes. pour celles et ceux qui n'ont pas peur de sortir des sentiers battus pour les femmes comme pour les hommes57,00 €*Shipping: 3,45 €Secure redirect to the provider


-
What exactly is TPM 2.0?
TPM 2.0, which stands for Trusted Platform Module 2.0, is a hardware-based security feature that provides a secure foundation for various security functions, such as encryption, authentication, and key management. It is a microcontroller that is typically integrated into computer systems to enhance security by securely storing sensitive information, such as encryption keys, digital certificates, and passwords. TPM 2.0 helps protect against various security threats, including unauthorized access, malware attacks, and data breaches, by providing a secure environment for sensitive data and cryptographic operations. **
-
How do I activate TPM?
To activate TPM (Trusted Platform Module) on your computer, you will need to access the BIOS or UEFI settings. Restart your computer and enter the BIOS/UEFI by pressing a specific key (usually F2, F10, or Del) during the boot-up process. Look for the TPM settings in the security or advanced settings section and enable TPM. Save the changes and exit the BIOS/UEFI settings. TPM should now be activated on your computer. **
-
Does it support TPM 2.0?
Yes, the device supports TPM 2.0. TPM (Trusted Platform Module) 2.0 is a security feature that provides hardware-based security functions, such as cryptographic keys and secure boot, to help protect the device from unauthorized access and tampering. This ensures that the device has a secure foundation for running trusted applications and protecting sensitive data. **
-
How can one delete TPM?
To delete TPM (Trusted Platform Module) on a computer, you would need to access the computer's BIOS or UEFI settings. Once in the settings, you can navigate to the security or TPM section and find the option to clear or reset the TPM. This will remove any existing TPM data and settings from the computer. It's important to note that deleting TPM may have implications for the computer's security and functionality, so it should only be done if necessary and with caution. **
How can I update TPM?
To update TPM (Trusted Platform Module), you can follow these steps: 1. Check for TPM firmware updates on the manufacturer's website or through the device's management software. 2. Download the latest TPM firmware update and follow the instructions provided by the manufacturer for installation. 3. Ensure that your device is connected to a stable power source and that all other applications are closed during the update process. 4. Restart your device after the update is complete to ensure that the changes take effect. It's important to regularly check for TPM updates to ensure that your device has the latest security features and bug fixes. **
Which one fits with TPM 20?
TPM 2.0 (Trusted Platform Module 2.0) is a hardware-based security solution that is designed to provide a secure foundation for various computing devices. It is typically integrated into the motherboard of a device and provides features such as secure boot, cryptographic key generation and storage, and hardware-based device authentication. TPM 2.0 is designed to enhance the security of devices and protect against various types of attacks, making it a suitable choice for organizations and individuals looking to secure their computing infrastructure. **
Top-Angebote
Products related to Tpm:
-
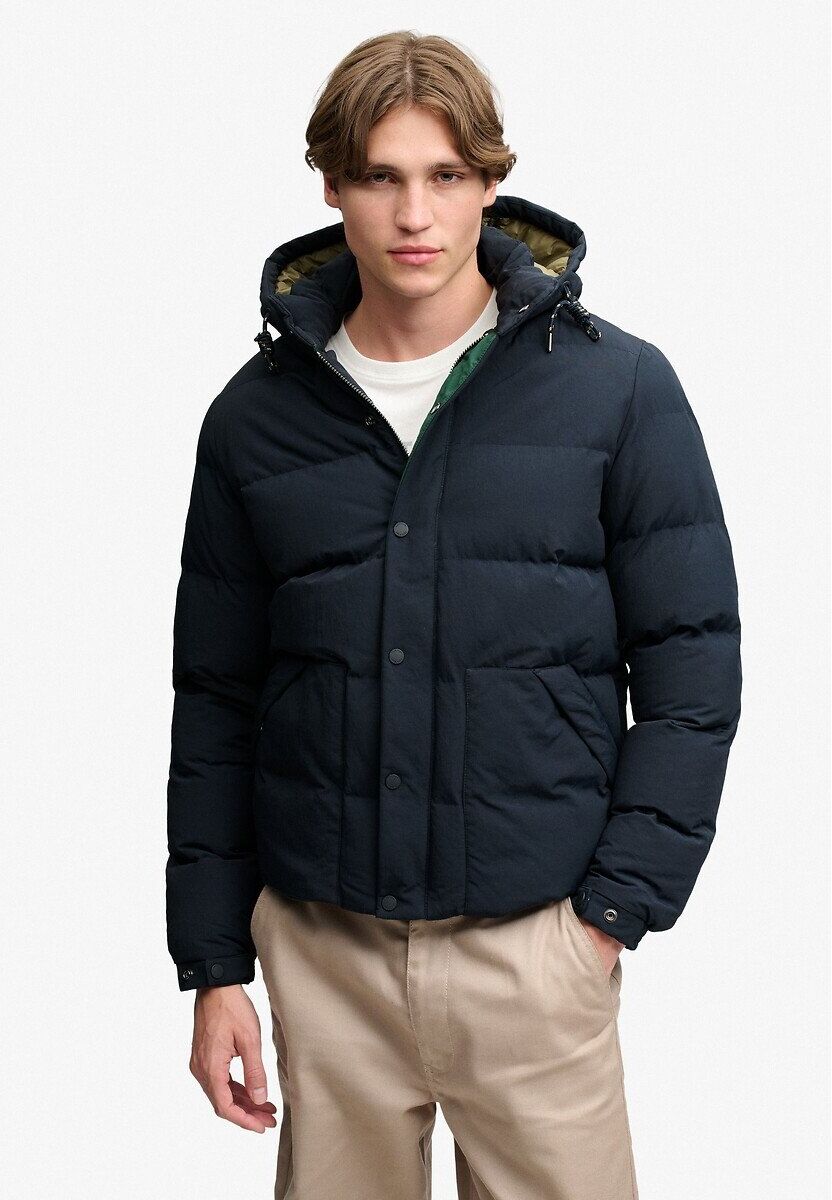
SUPERDRY Doudoune outdoor EverestDétails produit • Longueur : court • Col montant • Fermeture zippée • Capuche fixe réglable par cordon • 2 poches biais • Poignets réglables par bouton-pressions Composition et Entretien • Matière principale : 100% polyester • Doublure : 100% polyester • Garnissage : 100% polyester • Température de lavage 30° cycle délicat • Ne pas repasser / blanchiment interdit • Ne pas sécher en tambour • Pas de nettoyage à sec149,99 €*Shipping: 3,99 €Secure redirect to the provider
-
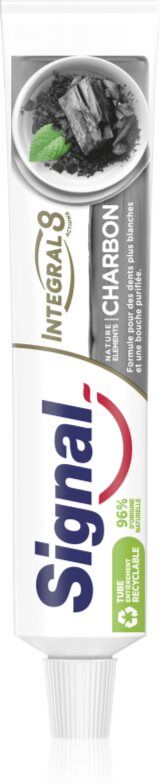
Signal Natural Elements Integral 8 Charcoal dentifrice Charcoal 75 mlSignal Natural Elements Integral 8 Charcoal, 75 ml, Dentifrices mixte, Le dentifrice Signal Natural Elements Integral 8Charcoal assure un soin complet de vos dents et de vos gencives. Il nettoie la plaque dentaire et les restes d’aliments de vos dents, il prend également soin de la gencive et des muqueuses buccales. Le produit : nettoie parfaitement les dents prend soin des gencives limite la formation de plaque dentaire Mode d’emploi : Nettoyez vos dents au moins 2 x par jour avec une brosse de qualité. Appliquez une quantité raisonnable de dentifrice sur la brosse à dents et nettoyez les dents pendant au moins 2 minutes. Rincez ensuite parfaitement votre cavité buccale.4,10 €*Shipping: 3,45 €Secure redirect to the provider
-
vidaXL Tapis de cuisine lavable texte Cooking 45x150 cm veloursCe tapis de cuisine est extrêmement doux et moelleux, et son design élégant attire tous les regards dans votre intérieur. Matériau durable : le dessus du tapis de cuisine est recouvert d'un tissu de velours doux qui absorbe rapidement l'eau et la saleté. La base en latex antidérapante assure que le tapis de cuisine adhère fermement au sol pour plus de sécurité. Lavable en machine : vous pouvez facilement nettoyer le tapis de sol de cuisine car il est lavable en machine. Rangement pratique : le tapis est flexible et peut être facilement enroulé pour le rangement et le transport.23,80 €*Shipping: 0,00 €Secure redirect to the provider
-
Smoking Hot van Kilian Uniseks Eau de Parfum 50mlSmoking Hot van By Kilian is een Oriëntaalse Kruidige geur voor dames en heren. Dit is een nieuwe geur. Smoking Hot werd gelanceerd in 2023. De neus achter deze geur is Mathieu Nardin. Topnoten zijn Appel, Kaneel en Rook; hartnoten zijn Tabak, Vanille en Mos; basisnoten zijn Bourbon Vanille, Orcanoxandtrade;, Zoethout, Iso E Super en Muskaatsalie.185,00 €*Shipping: 0,00 €Secure redirect to the provider
-
What is BitLocker TPM?
BitLocker TPM (Trusted Platform Module) is a security feature in Windows operating systems that uses a hardware component called TPM to provide enhanced protection for data stored on a computer's hard drive. TPM is a microchip that securely stores encryption keys, passwords, and other sensitive information to help protect against unauthorized access to the system. When BitLocker TPM is enabled, the encryption keys are securely stored in the TPM, making it more difficult for attackers to access the data even if they physically remove the hard drive from the computer. **
-
Can't you activate TPM?
Yes, TPM (Trusted Platform Module) can be activated on compatible devices through the device's BIOS settings. However, not all devices have TPM built-in, so it's important to check the device's specifications to see if TPM is available. Once activated, TPM provides hardware-based security features such as secure boot, device encryption, and key management to help protect sensitive data and ensure the integrity of the system. **
-
What exactly is TPM 2.0?
TPM 2.0, which stands for Trusted Platform Module 2.0, is a hardware-based security feature that provides a secure foundation for various security functions, such as encryption, authentication, and key management. It is a microcontroller that is typically integrated into computer systems to enhance security by securely storing sensitive information, such as encryption keys, digital certificates, and passwords. TPM 2.0 helps protect against various security threats, including unauthorized access, malware attacks, and data breaches, by providing a secure environment for sensitive data and cryptographic operations. **
-
How do I activate TPM?
To activate TPM (Trusted Platform Module) on your computer, you will need to access the BIOS or UEFI settings. Restart your computer and enter the BIOS/UEFI by pressing a specific key (usually F2, F10, or Del) during the boot-up process. Look for the TPM settings in the security or advanced settings section and enable TPM. Save the changes and exit the BIOS/UEFI settings. TPM should now be activated on your computer. **
Similar search terms for Tpm
-
bdk Parfums Rouge Smoking Eau de Parfum mixte 50 mlbdk Parfums Rouge Smoking, 50 ml, Eaux de Parfum mixte, Fraîche et mystérieuse, moderne et à la fois hors du temps ! Il s'agit bien de l'eau de parfum mixte bdk Parfums Rouge Smoking dont la composition parfumée est parfaite pour les femmes comme pour les hommes. pour celles et ceux qui n'ont pas peur de sortir des sentiers battus pour les femmes comme pour les hommes125,60 €*Shipping: 3,45 €Secure redirect to the provider
-
bdk Parfums Rouge Smoking Eau de Parfum mixte 10 mlbdk Parfums Rouge Smoking, 10 ml, Eaux de Parfum mixte, Fraîche et mystérieuse, moderne et à la fois hors du temps ! Il s'agit bien de l'eau de parfum mixte bdk Parfums Rouge Smoking dont la composition parfumée est parfaite pour les femmes comme pour les hommes. pour celles et ceux qui n'ont pas peur de sortir des sentiers battus pour les femmes comme pour les hommes57,00 €*Shipping: 3,45 €Secure redirect to the provider
-
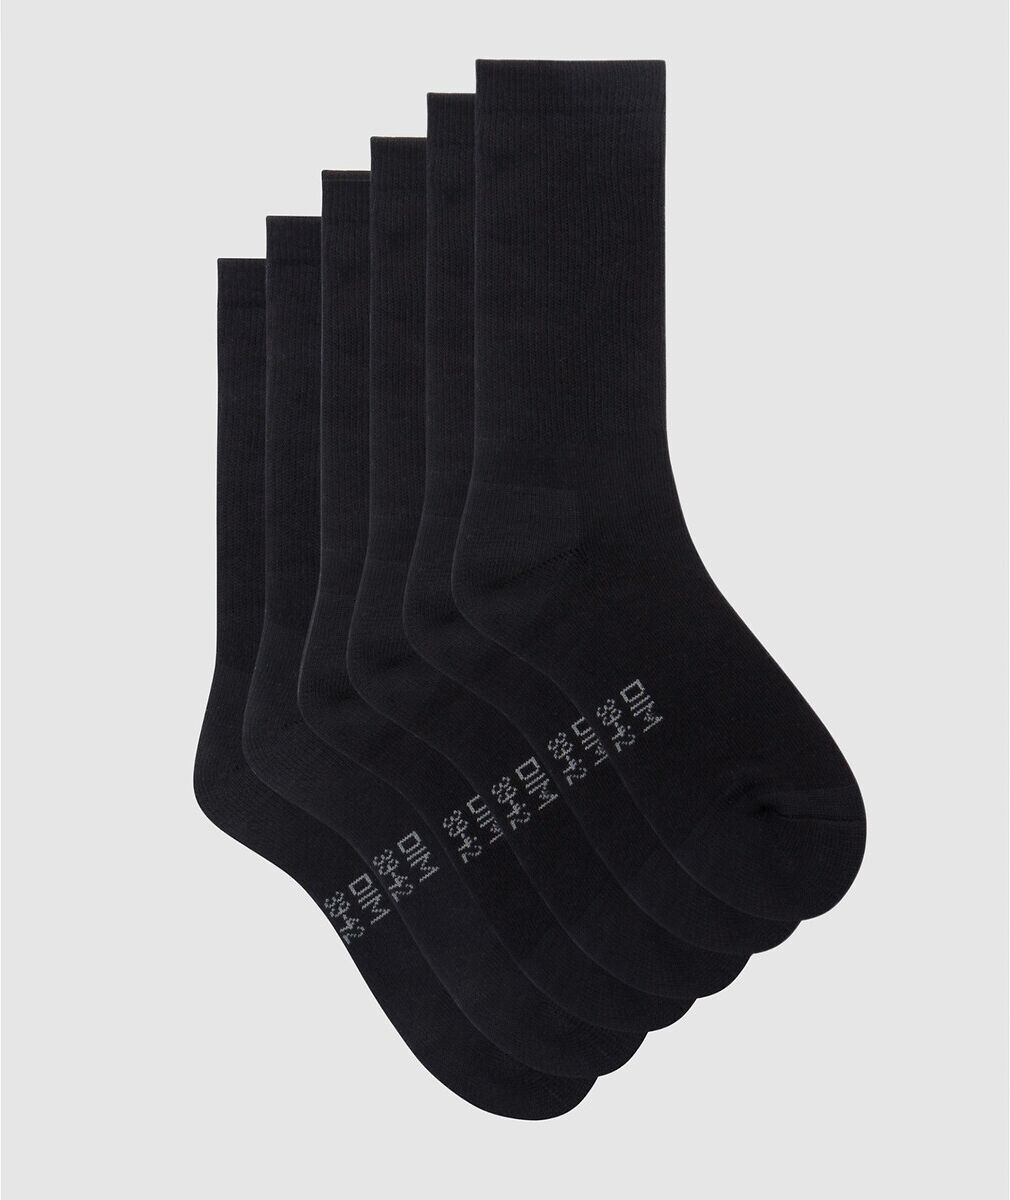
DIM Lot de 3 paires de chaussettes OutdoorDétails produit • Lot de 3 • Mi-chaussettes Composition et Entretien • 72% coton, 24% polyester, 3% elastodiene, 1% élasthanne • Pour l'entretien, merci de vous référer aux indications figurant sur l'étiquette du produit • OEKO-TEX® Standard 100. La labellisation OEKO-TEX® Standard 100 contrôle les substances nocives des produits textiles via un label indépendant et international. Fiche produit relative aux qualités et caractéristiques environnementales • Origine de fabrication (tissage, teinture, confection) : Chine Dernière mise à jour des informations : 02/04/202615,38 €*Shipping: 3,99 €Secure redirect to the provider
-
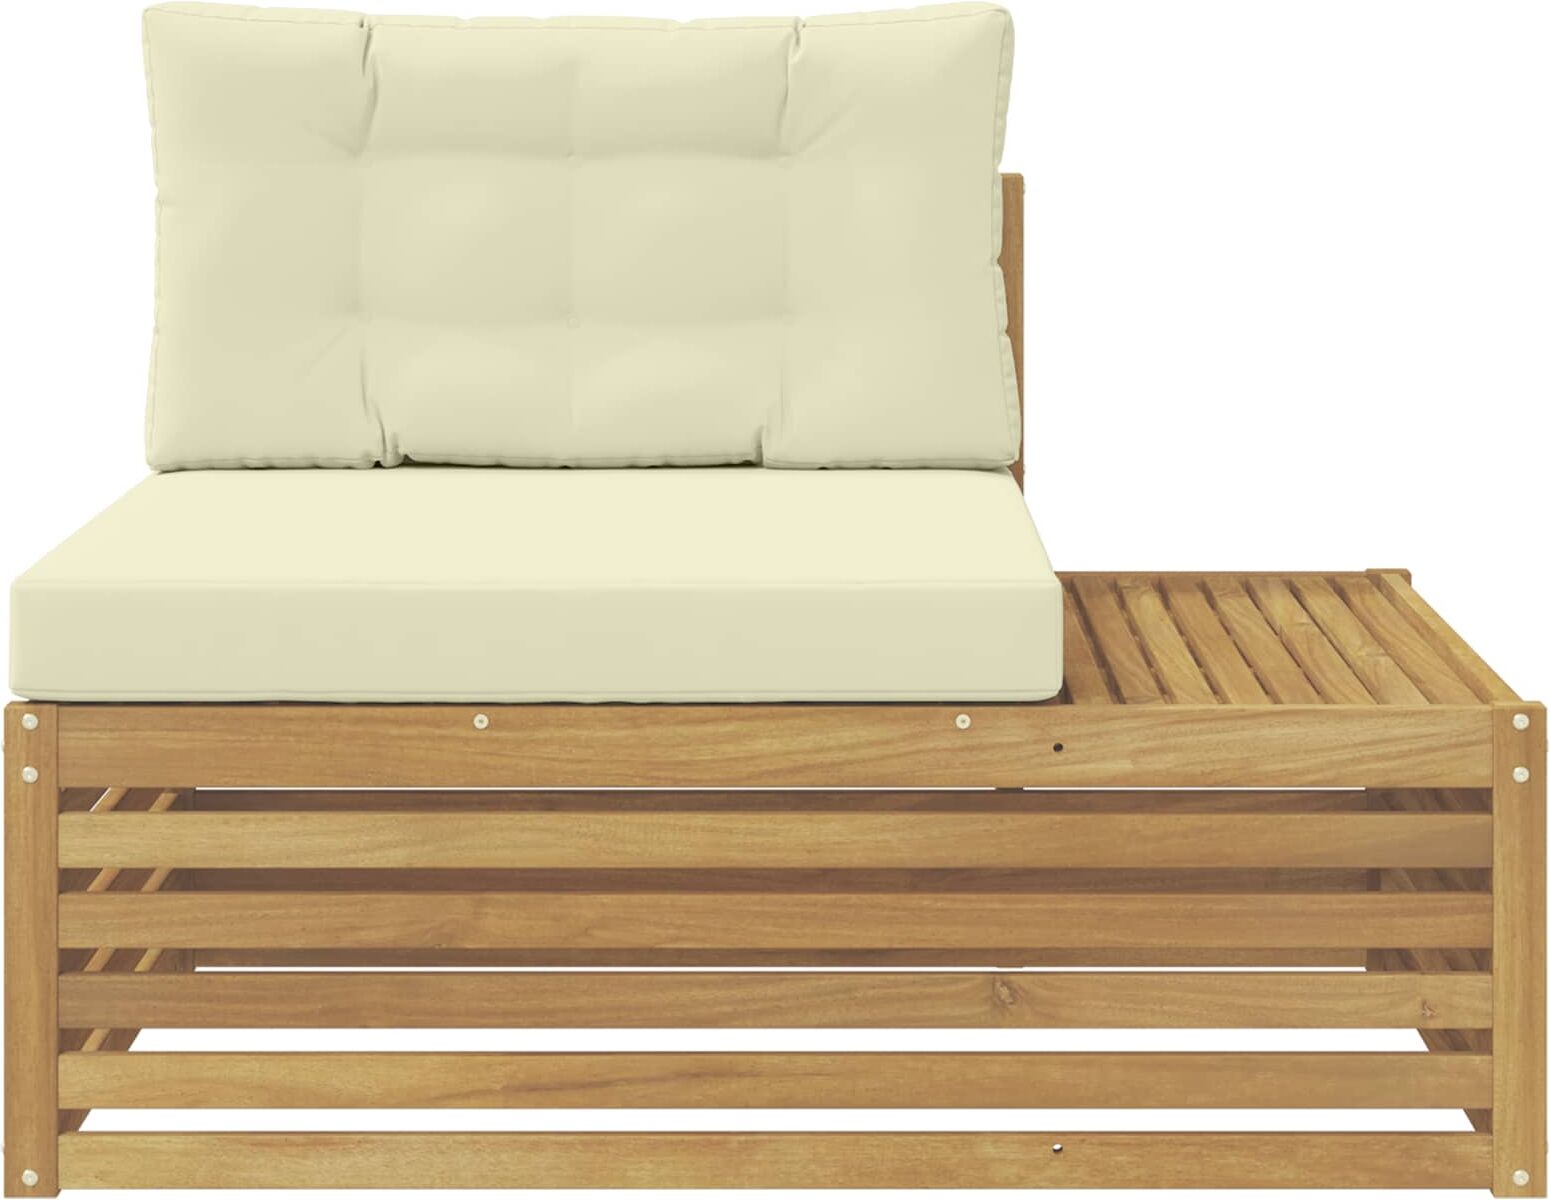
vidaXL Outdoor End sofa Bois d'Acacia Massif BlancCe mobilier d'extérieur s'intègre facilement dans n'importe quel jardin, apportant une touche contemporaine qui marie simplicité et praticité. Fabriqué en bois massif d'acacia, ses lignes nettes en font un point focal sympa pour vos espaces extérieurs. Il est conçu pour résister aux intempéries et s'adapte sans effort à différents décors tout en embellissant l'ensemble de l'espace. Bois d'acacia massif : 100% en bois d'acacia robuste, ce meuble a une durabilité incroyable et résiste bien aux conditions extérieures. Le grain naturel du bois y ajoute une touche d'élégance, ce qui en fait un choix à la fois chic et pratique pour l'extérieur. Design polyvalent : Chaque pièce est pensée pour être flexible, s’ajustant facilement à divers agencements et besoins extérieurs. Ce design adaptable convient à plusieurs situations et cadres. Design à lattes moderne : Parfait pour les espaces modernes, le design à lattes améliore la circulation de l’air, permettant au bois de sécher plus vite après la pluie tout en garantissant confort et durabilité. Fonctionnalité extérieure : Ce meuble est conçu pour un usage extérieur et résiste à tous les types de météo tout en gardant sa beauté et sa praticité. Idéal pour les jardins, patios et tous les espaces extérieurs. Entretien facile : Pour qu'il reste en bon état, il suffit d’essuyer la surface avec un chiffon humide pour enlever la poussière et les salissures. Cette routine simple aide à préserver son apparence avec le temps.148,99 €*Shipping: 0,00 €Secure redirect to the provider
-
Does it support TPM 2.0?
Yes, the device supports TPM 2.0. TPM (Trusted Platform Module) 2.0 is a security feature that provides hardware-based security functions, such as cryptographic keys and secure boot, to help protect the device from unauthorized access and tampering. This ensures that the device has a secure foundation for running trusted applications and protecting sensitive data. **
-
How can one delete TPM?
To delete TPM (Trusted Platform Module) on a computer, you would need to access the computer's BIOS or UEFI settings. Once in the settings, you can navigate to the security or TPM section and find the option to clear or reset the TPM. This will remove any existing TPM data and settings from the computer. It's important to note that deleting TPM may have implications for the computer's security and functionality, so it should only be done if necessary and with caution. **
-
How can I update TPM?
To update TPM (Trusted Platform Module), you can follow these steps: 1. Check for TPM firmware updates on the manufacturer's website or through the device's management software. 2. Download the latest TPM firmware update and follow the instructions provided by the manufacturer for installation. 3. Ensure that your device is connected to a stable power source and that all other applications are closed during the update process. 4. Restart your device after the update is complete to ensure that the changes take effect. It's important to regularly check for TPM updates to ensure that your device has the latest security features and bug fixes. **
-
Which one fits with TPM 20?
TPM 2.0 (Trusted Platform Module 2.0) is a hardware-based security solution that is designed to provide a secure foundation for various computing devices. It is typically integrated into the motherboard of a device and provides features such as secure boot, cryptographic key generation and storage, and hardware-based device authentication. TPM 2.0 is designed to enhance the security of devices and protect against various types of attacks, making it a suitable choice for organizations and individuals looking to secure their computing infrastructure. **
* All prices are inclusive of VAT and, if applicable, plus shipping costs. The offer information is based on the details provided by the respective shop and is updated through automated processes. Real-time updates do not occur, so deviations can occur in individual cases. ** Note: Parts of this content were created by AI.